Brian's Virtually Useful Blog

When you install ESX

July 20, 2009
The only changes I recommend are these.

800 MB for Service Console (for HP ESX mgmnt, for Backups)
1600 MB for Page File (should always be 2x SC above)
1500mhz reserved for Service Console (for backups, misc)

UPS-Tastic

June 19, 2009
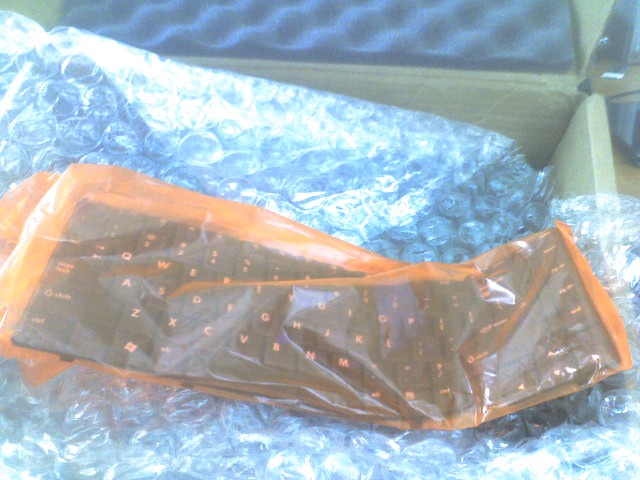
These guys must hate us..or be Jim Carey in Ace Ventura.


EDIT #1

Thank god I didn't need another free Dell keyboard.

EDIT #2

No, its not a new type of fancy ergonomic keyboard.

EDIT #3

No, its not a Dell keyboard, its an HP laptop keyboard, but know that only makes me sad and breaking the free Dell keyboards just doesn't...

Scanning with nmap

June 8, 2009
For local subnet
nmap [-n] -sP -PR -T[4,5] --max-retries[0,1]
-- host - timeout 4000 -oG *.*.*.*

For scans on routable subnet (icmp echo)
nmap [-n] -sP -PE -T[4,5] --max-retries [0,1]
--host-timeout 10000 -oG *.*.*.*

Red is for recommended value

ESX 4 HA Errors

May 30, 2009 · 1 comment
So I had read ESX4 was better about HA setup than 3.x. I was in the beta, but didn't have the chance to test HA. So after upgrading the production cluster to ESX4, HA was broken again.

Enabling HA gave the error:
"Cannot complete the configuration of HA agent on the host. See the task for details for addional information. Misconfiguration in the host network setup."

After poking around for a while, I realized that one host had a bad Default Gateway (off my 1) setup. After correcting that, HA works like a champ.

I did also fix the fact that one of my /etc/hosts files had my VMOTION service console IP and not the correct primary SC IP.

But its all good new..

ESX 4 is really nice..

ISA 2006 Firewall Service won't start

May 30, 2009
I get an error just like this:
==============================================================================
Event Type: Error
Event Source: Service Control Manager
Event Category: None
Event ID: 7001
Date: 2/20/2008
Time: 10:19:44 AM
User: N/A
Computer: ISA
Description:
The Microsoft Firewall service depends on the MSSQL$MSFW service which failed to start because of the following error:
The operation completed successfully.
For more information, see Help and Support Center at http://go.microsoft.com/fwlink/events.asp.
--------------------------
and when i try to start Microsoft Firewall service it says: " Could not start the Microsoft Firewall service on Local Computer.

Error 1068: The dependency service or group failed to start."

also the other automatic service on which Microsoft Firewall service is dependant is stopped and when i try to start that service it says "The MSSQL$MSFW service on Local Computer started and then stopped. Some services stop automatically if they have no work to do, for example, the Performance Logs and Alerts service."
================================================================================

Following these articles
http://forums.isaserver.org/m_2002062646/printable.htm
and
http://www.tech-archive.net/Archive/Windows/microsoft.public.windows.server.sbs/2008-07/msg00461.html

they say there is a problem writing to the logs, and that's why I can't start the service. After changing the logging types, and many other changes, the final fix was to do as others had said. Export your ISA config, uninstall and reinstall ISA, and blamo, everything works again.

Things I needed to Deploy SSTP (windows 2008 HTTPS/SSL VPN)

May 21, 2009


Step-by-Step Guide: Deploying SSTP Remote Access

Do you want to change the certificate used by the SSTP server - Read how

Getting Certificate from third party Certificate Authorities for SSTP

Publishing SSTP based VPN server using ISA2006 Firewall

Registry entries that Routing and Remote Access adds in Windows Server 2008

How to debug SSTP specific connection failures

I’ll fill in some more blanks one I feel more comfortable with it.

However i’ll say so far MAKE SURE to open port 443 on your 2008 VPN server or this won’t work.

How to find and kill a hung VM on ESX 3.5

May 20, 2009

First you must find the PID

ps auxfww | grep Name_of_the_VM

Then kill it

Stop Soft Technique:

# vmware-cmd /path/to/config/file.vmx stop soft

Stop Hard Technique:
# vmware-cmd /path/to/config/file.vmx stop hard

kill Techniques:
# kill <pid>

If the above doesn't work you may need to issue a kill –9

# kill -9 <pid>

Thanks to This article I used to get my information.

http://communities.vmware.com/message/245617;jsessionid=AC54B73461657AECCF0CB98763CE2C2C

Issues using ISA 2006 for a back firewall

May 19, 2009

For some reason after reinstalling ISA 2006 as a back firewall, you can’t reach some machines on the DMZ network.  Without a long discussion for the routing reasons for this, The solution is to modify the ISA back firewall in order to disable the proxy on it.

To disable the Web Proxy filter for HTTP, do the following:

  1. In ISA Server Management, click the Firewall Policy node.
  2. On the Toolbox tab, click Protocols.
  3. Expand All Protocols, right-click HTTP, and then click Properties.
  4. Click the Parameters tab, and in Application Filters, clear Web Proxy Filter. Then click OK.
  5. Click Apply to update the firewall policy.